Setting Up Your Workspace in the New Dashboard
Audience. The account administrator of a workspace that uses the new dashboard.
Outcome. All six Company setup stages are done. Your Article 14 contacts are recorded, your reporting channel is published and verified, alerts go to the right people, your team has access, and your portal has received a report.
Why it matters. Article 14 of the CRA applies from 11 September 2026. The setup stages are the minimum a manufacturer needs before a report arrives. The new dashboard tracks each stage and shows the next one on the home page.
Time required. About 45 minutes. Stage 3 can take longer if someone else controls your company website.
Applies to. The new dashboard. To use it, switch on New interface in the top bar. For the classic dashboard, use SOP-01.
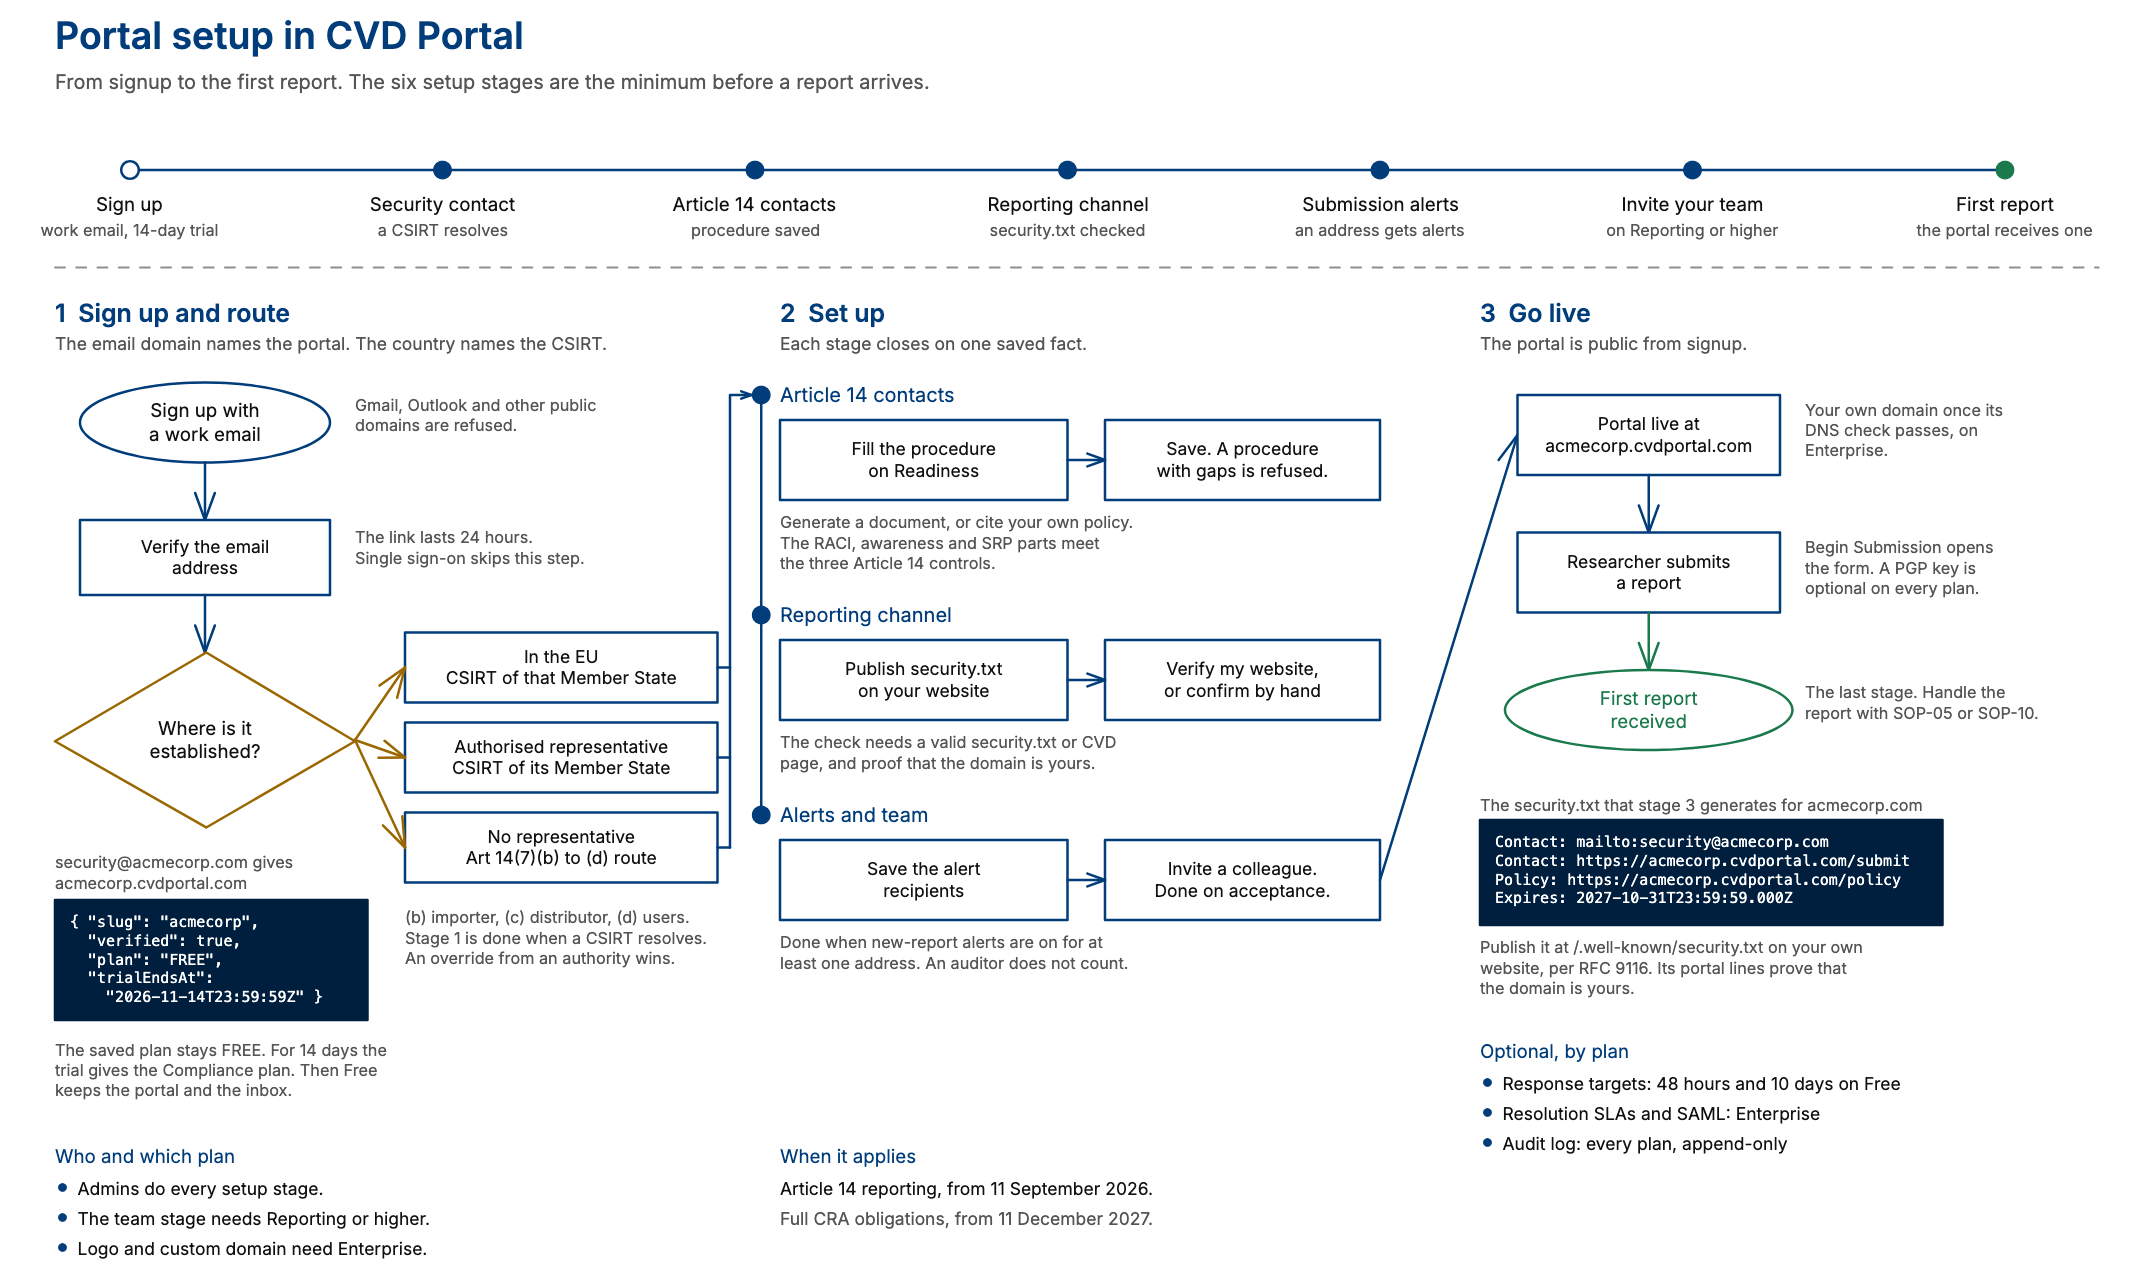
The flow at a glance
The diagram shows the six setup stages on one page, from signup to the first report. The classic dashboard uses the same settings, see SOP-01. The steps below explain each stage. Select the diagram to open it at full size. The example company is fictional.
Step 0. Find the setup row on the Overview
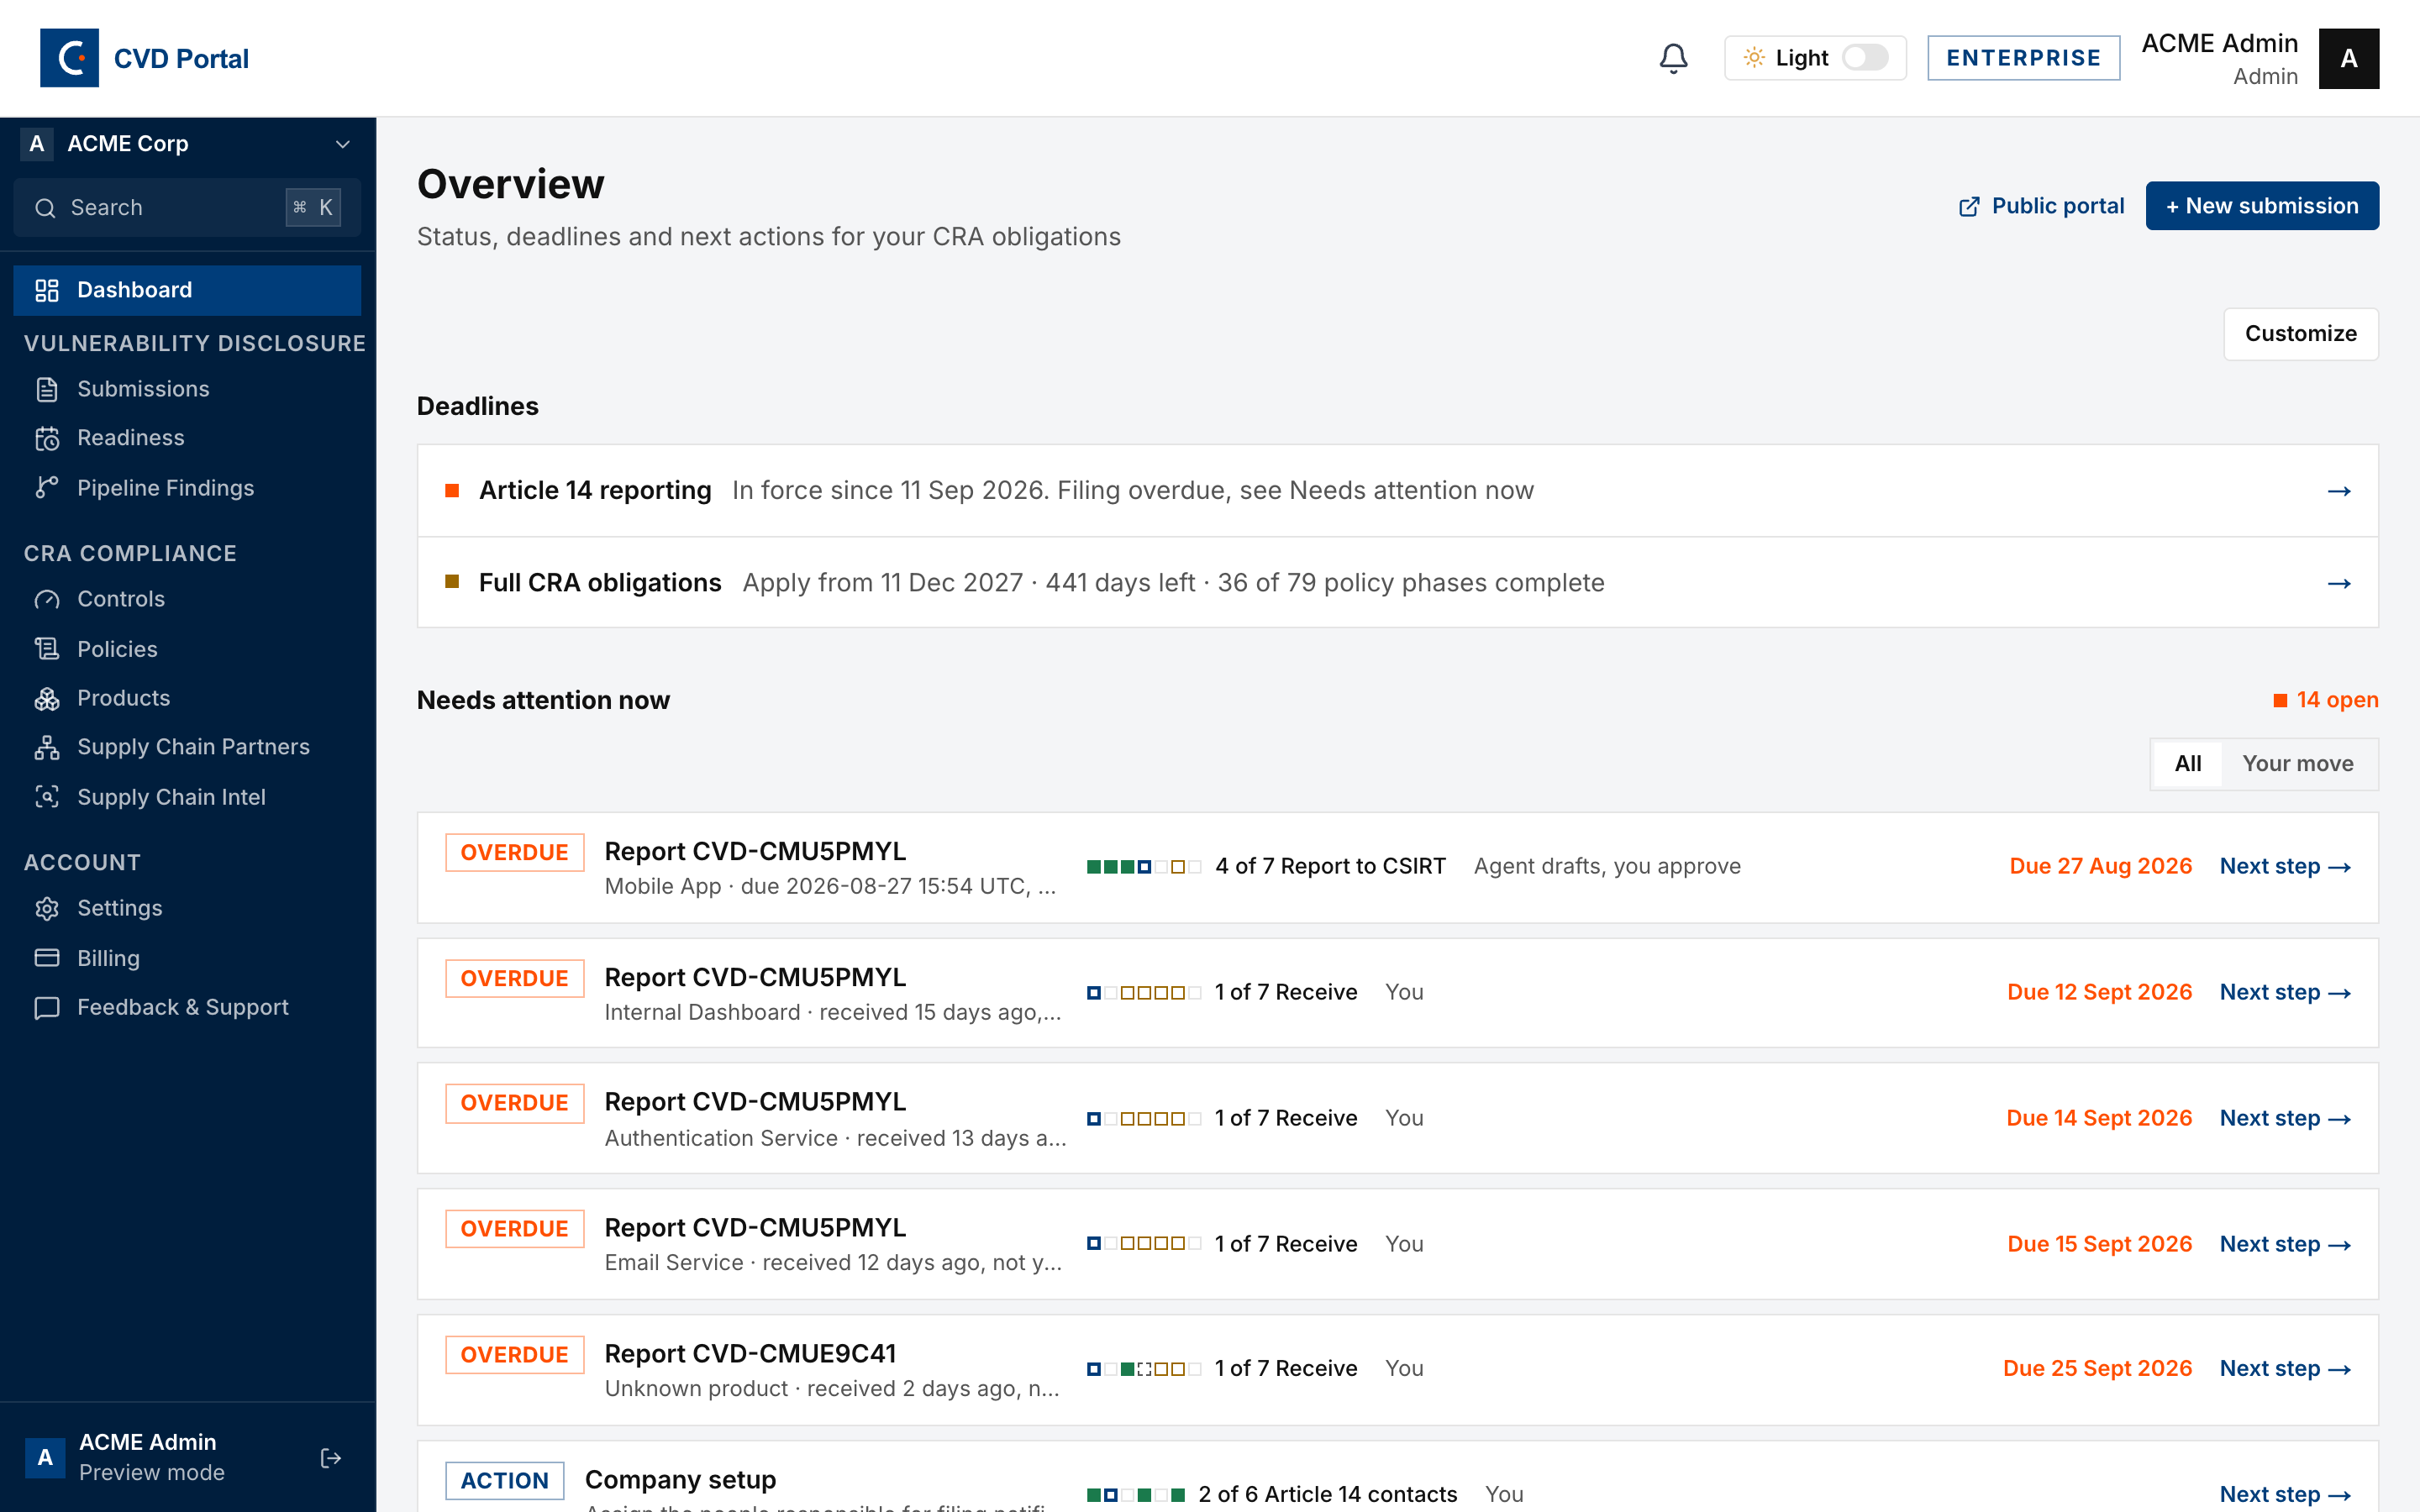
Open Dashboard. The Overview page shows your deadlines first, then Needs attention now.
The Full CRA obligations line shows the days left until 11 December 2027 and your progress, for example "36 of 79 CRA artifacts complete". The count is the unique CRA artifacts across all seven phases. Artifacts that the portal supplies always count as complete.
The Article 14 reporting line tells you what holds reporting back, and a click opens the page for that work. When it reads "0 of 5 reporting controls satisfied", the click opens Controls with only the open reporting controls. When only the September 2026 artifacts are missing, it opens them on the Groundwork tab of Readiness. When a filing is due, it opens Submissions. The 04 Reporting card below uses the same rule.
The Obligations cards show the five CRA obligation groups. Only 04 Reporting (Article 14) applies now, from 11 September 2026. The other four apply from 11 December 2027. Until then, a card for a later obligation that is not ready shows the grey status Applies 11 Dec 2027, not Action required. A card that is ready shows Ready, whatever its date.
The row Company setup, in the Account setup group, shows the current stage, for example "2 of 6 Article 14 contacts". On the Free plan there are five stages, because the team stage does not apply. The small bar shows one square per stage. A filled square is a done stage. The outlined square is the current stage.
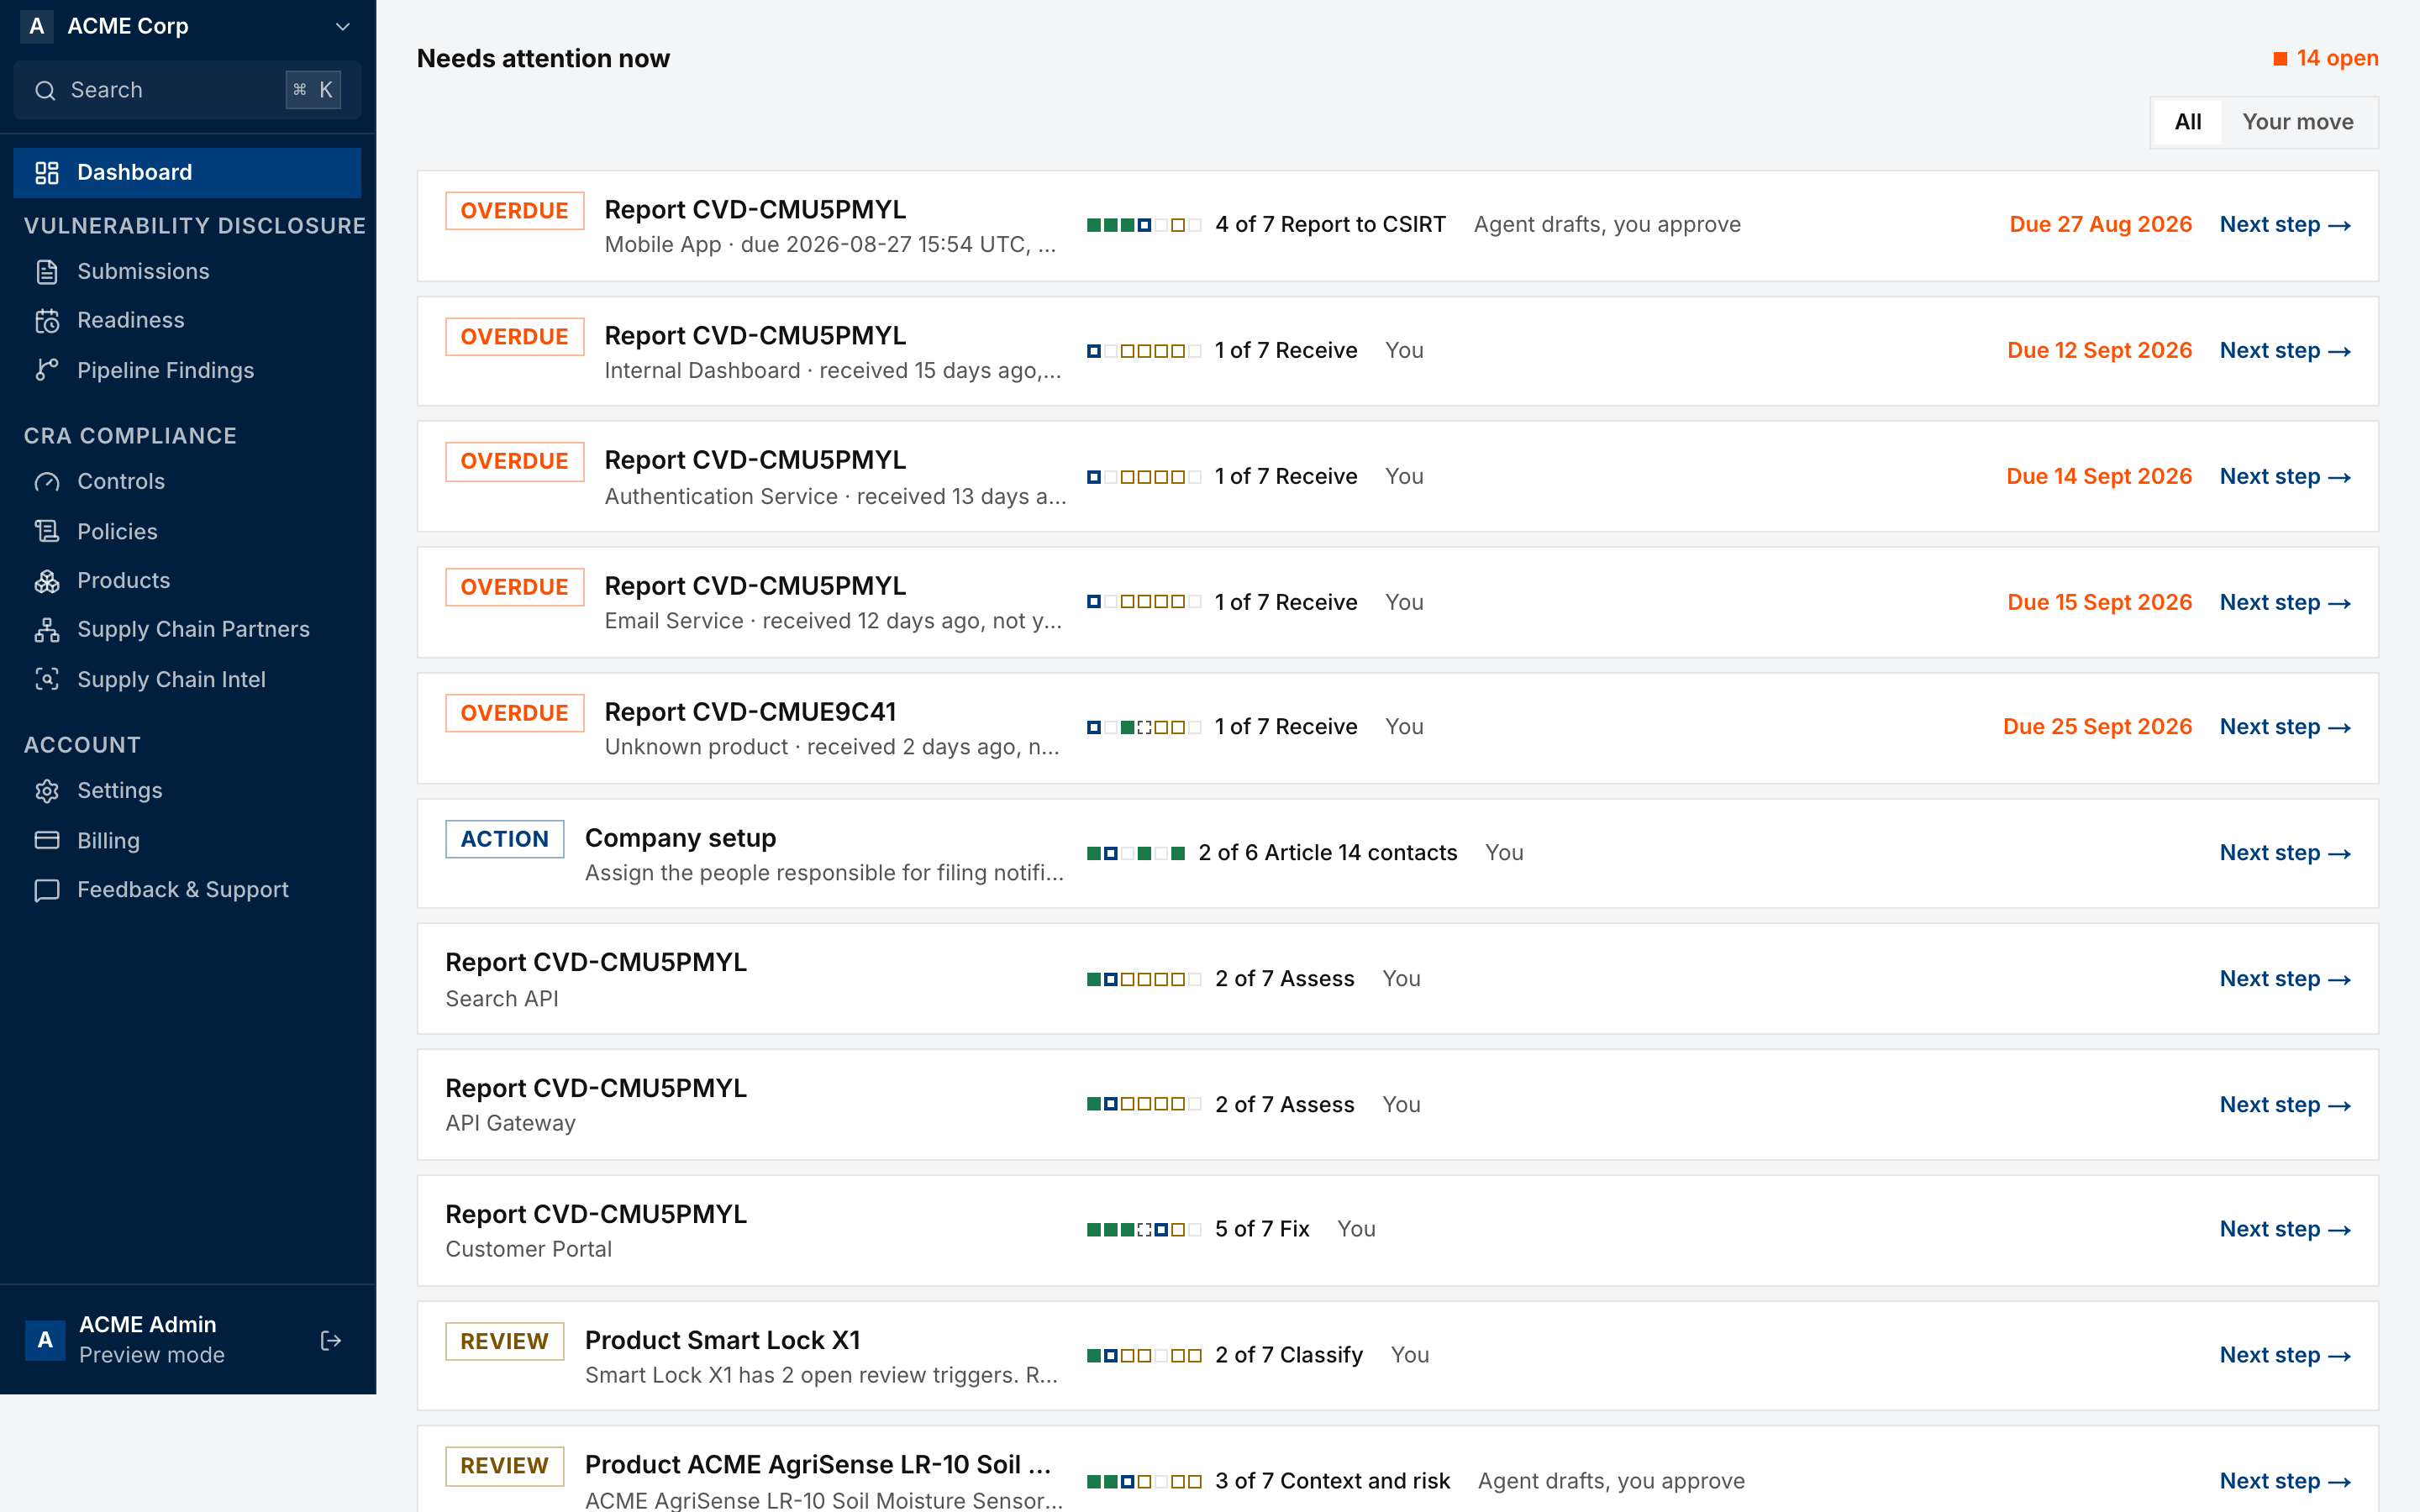
Click Next step on the row. The portal opens the page for the current stage. When all six stages are done, the row goes away.
Select Your move to show only the rows where you must act.
Step 1. Security contact and Article 14 details
Open Settings, then General. Go to Establishment & Article 14 reporting.
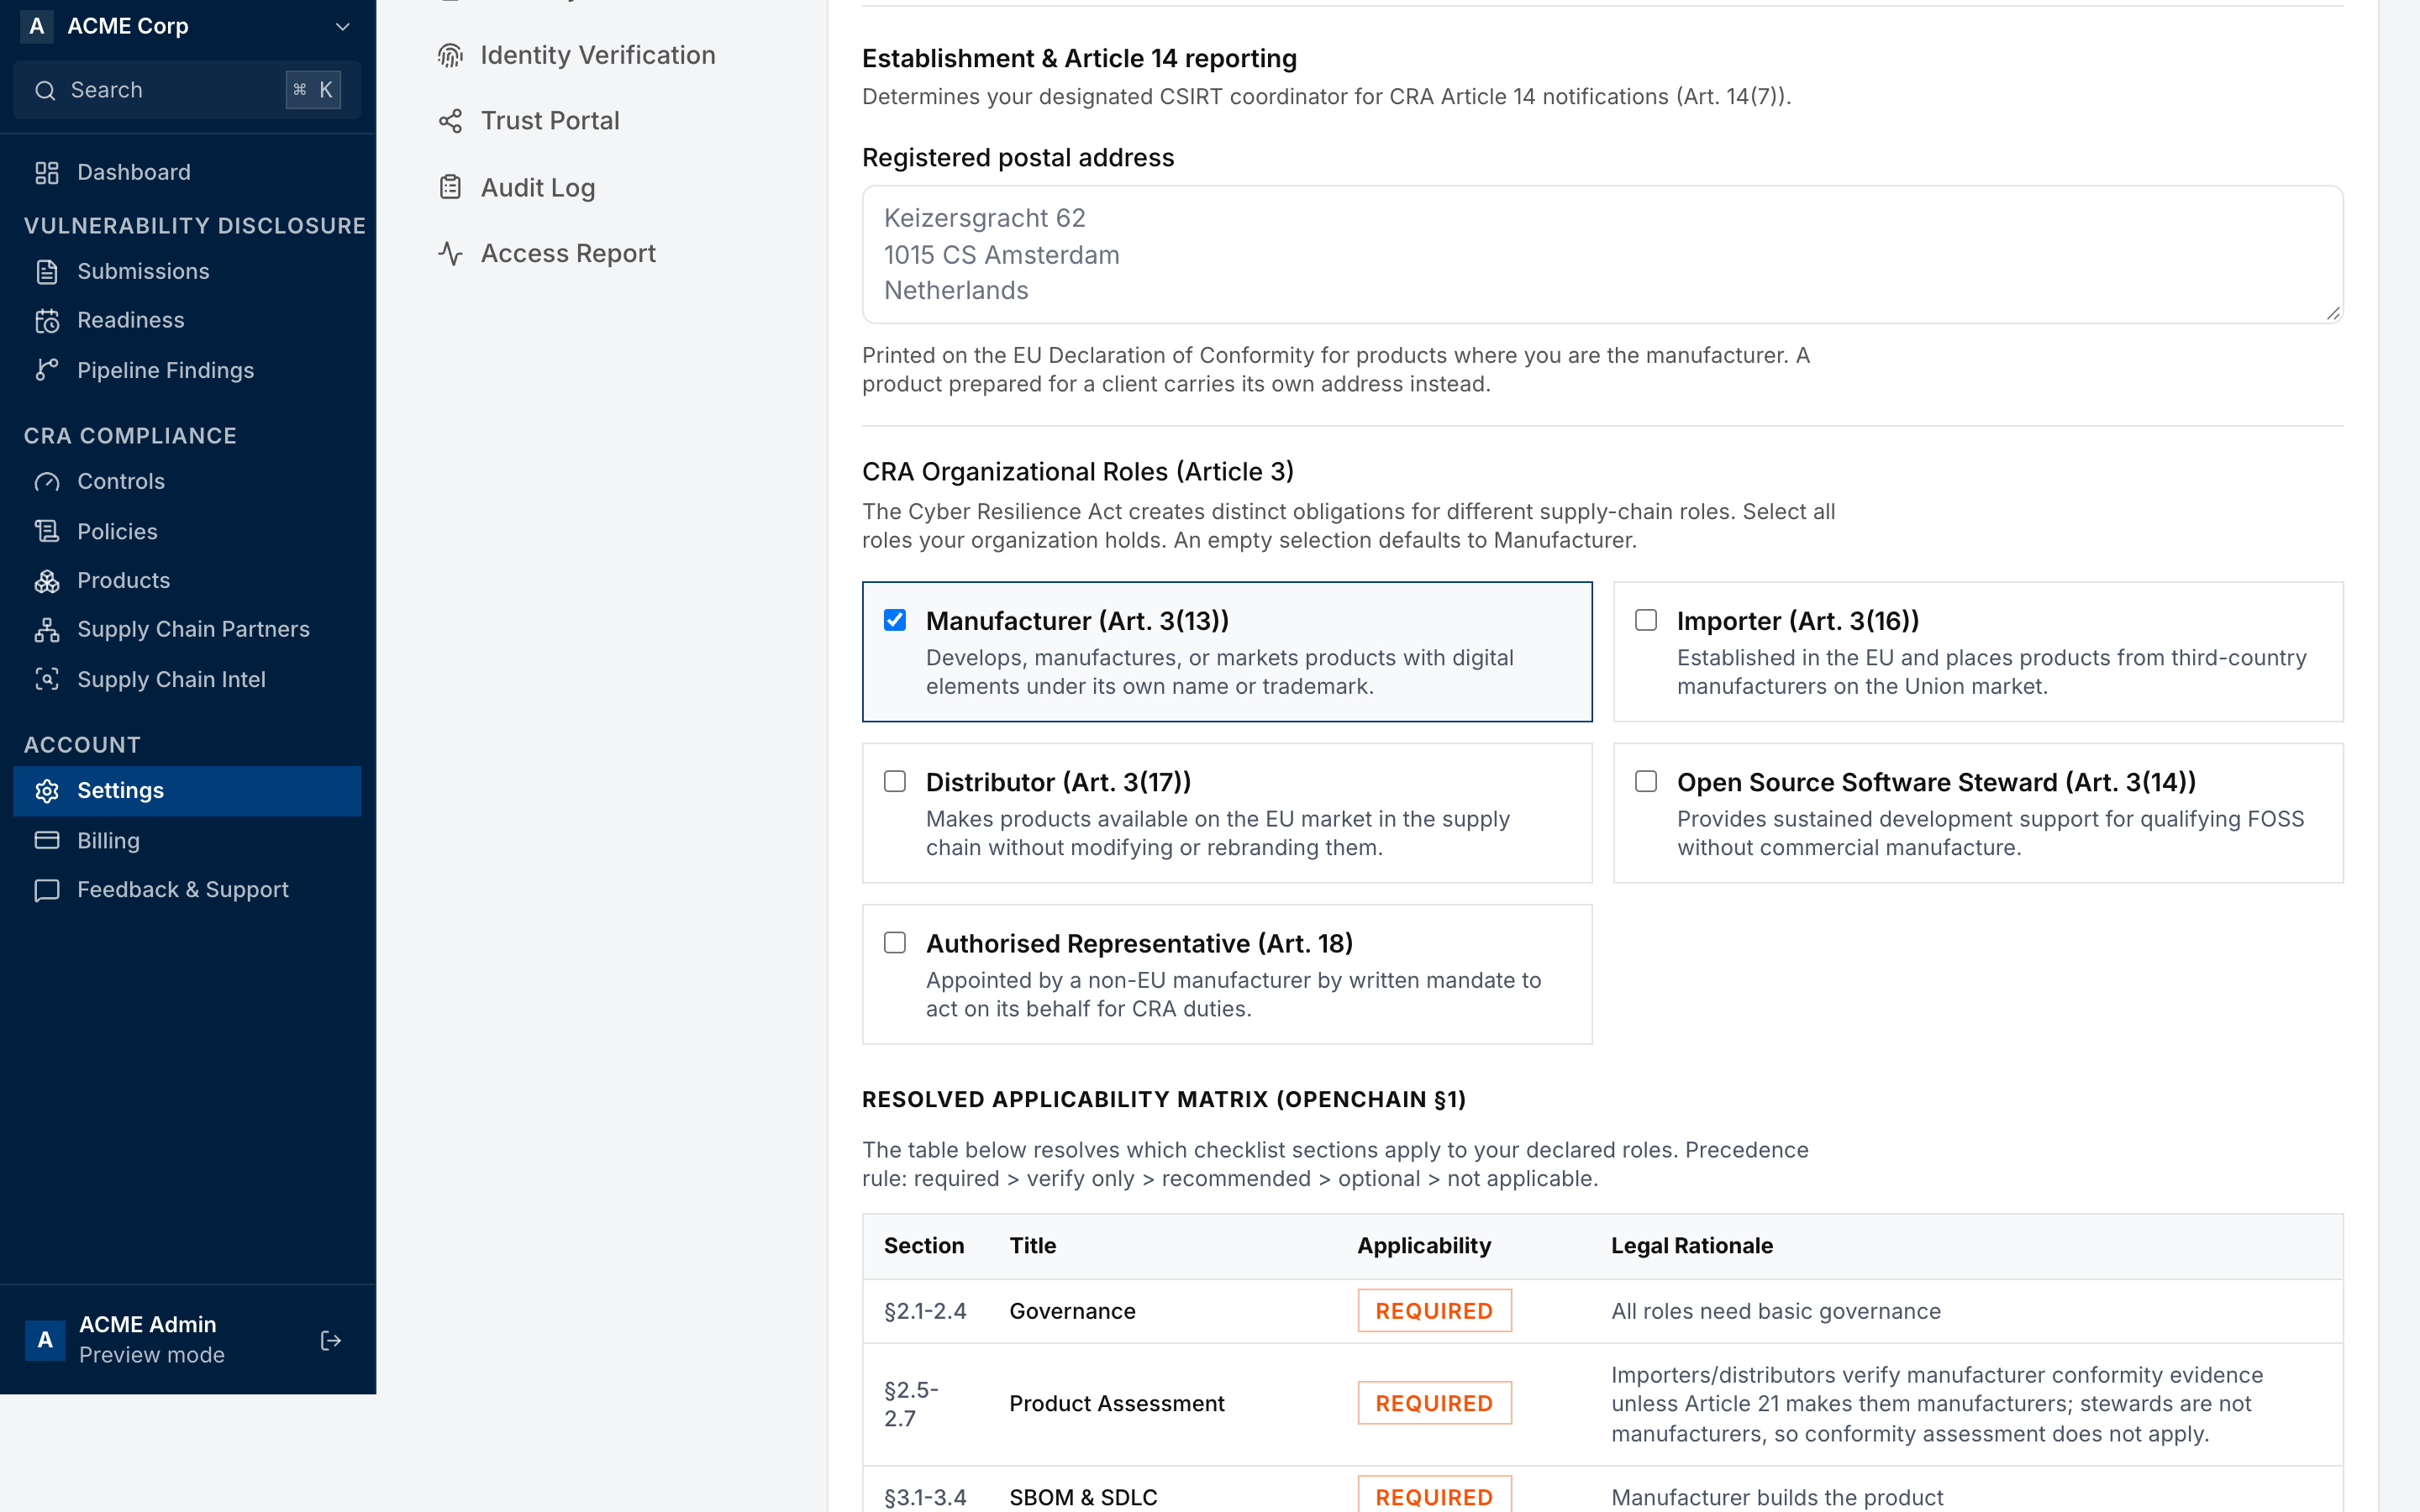
- Enter your registered postal address.
- Select every CRA role your company has. If you select none, the portal uses Manufacturer.
- In Place of establishment, select where your company is established.
- If it is in the EU, select the Member State of main establishment. Your drafts (the EU declaration of conformity, the Annex II user information and the Article 14 report) say that you are established in the EU only after you select it. Until then they show a placeholder.
- If it is not in the EU and you have an authorised representative, enter its name, email and Member State. An authorised representative is optional (Article 18(1)).
- If it is not in the EU and you have no authorised representative, select the CSIRT route (Article 14(7)) and its Member State. The route is the importer, the distributor or the users of most of your products.
- Click Save Changes.
Done when. The portal finds a national CSIRT for your company. That CSIRT receives your Article 14 notifications (Article 14(7)). The portal uses the Member State of main establishment, then the Member State of the authorised representative, then the CSIRT route. A representative with no Member State does not complete the stage. A Designated CSIRT override from a national authority wins over every route.
Step 2. Article 14 contacts
Open Readiness and select the Procedure tab (/readiness/procedure). The tab holds the Vulnerability Handling Procedure form.
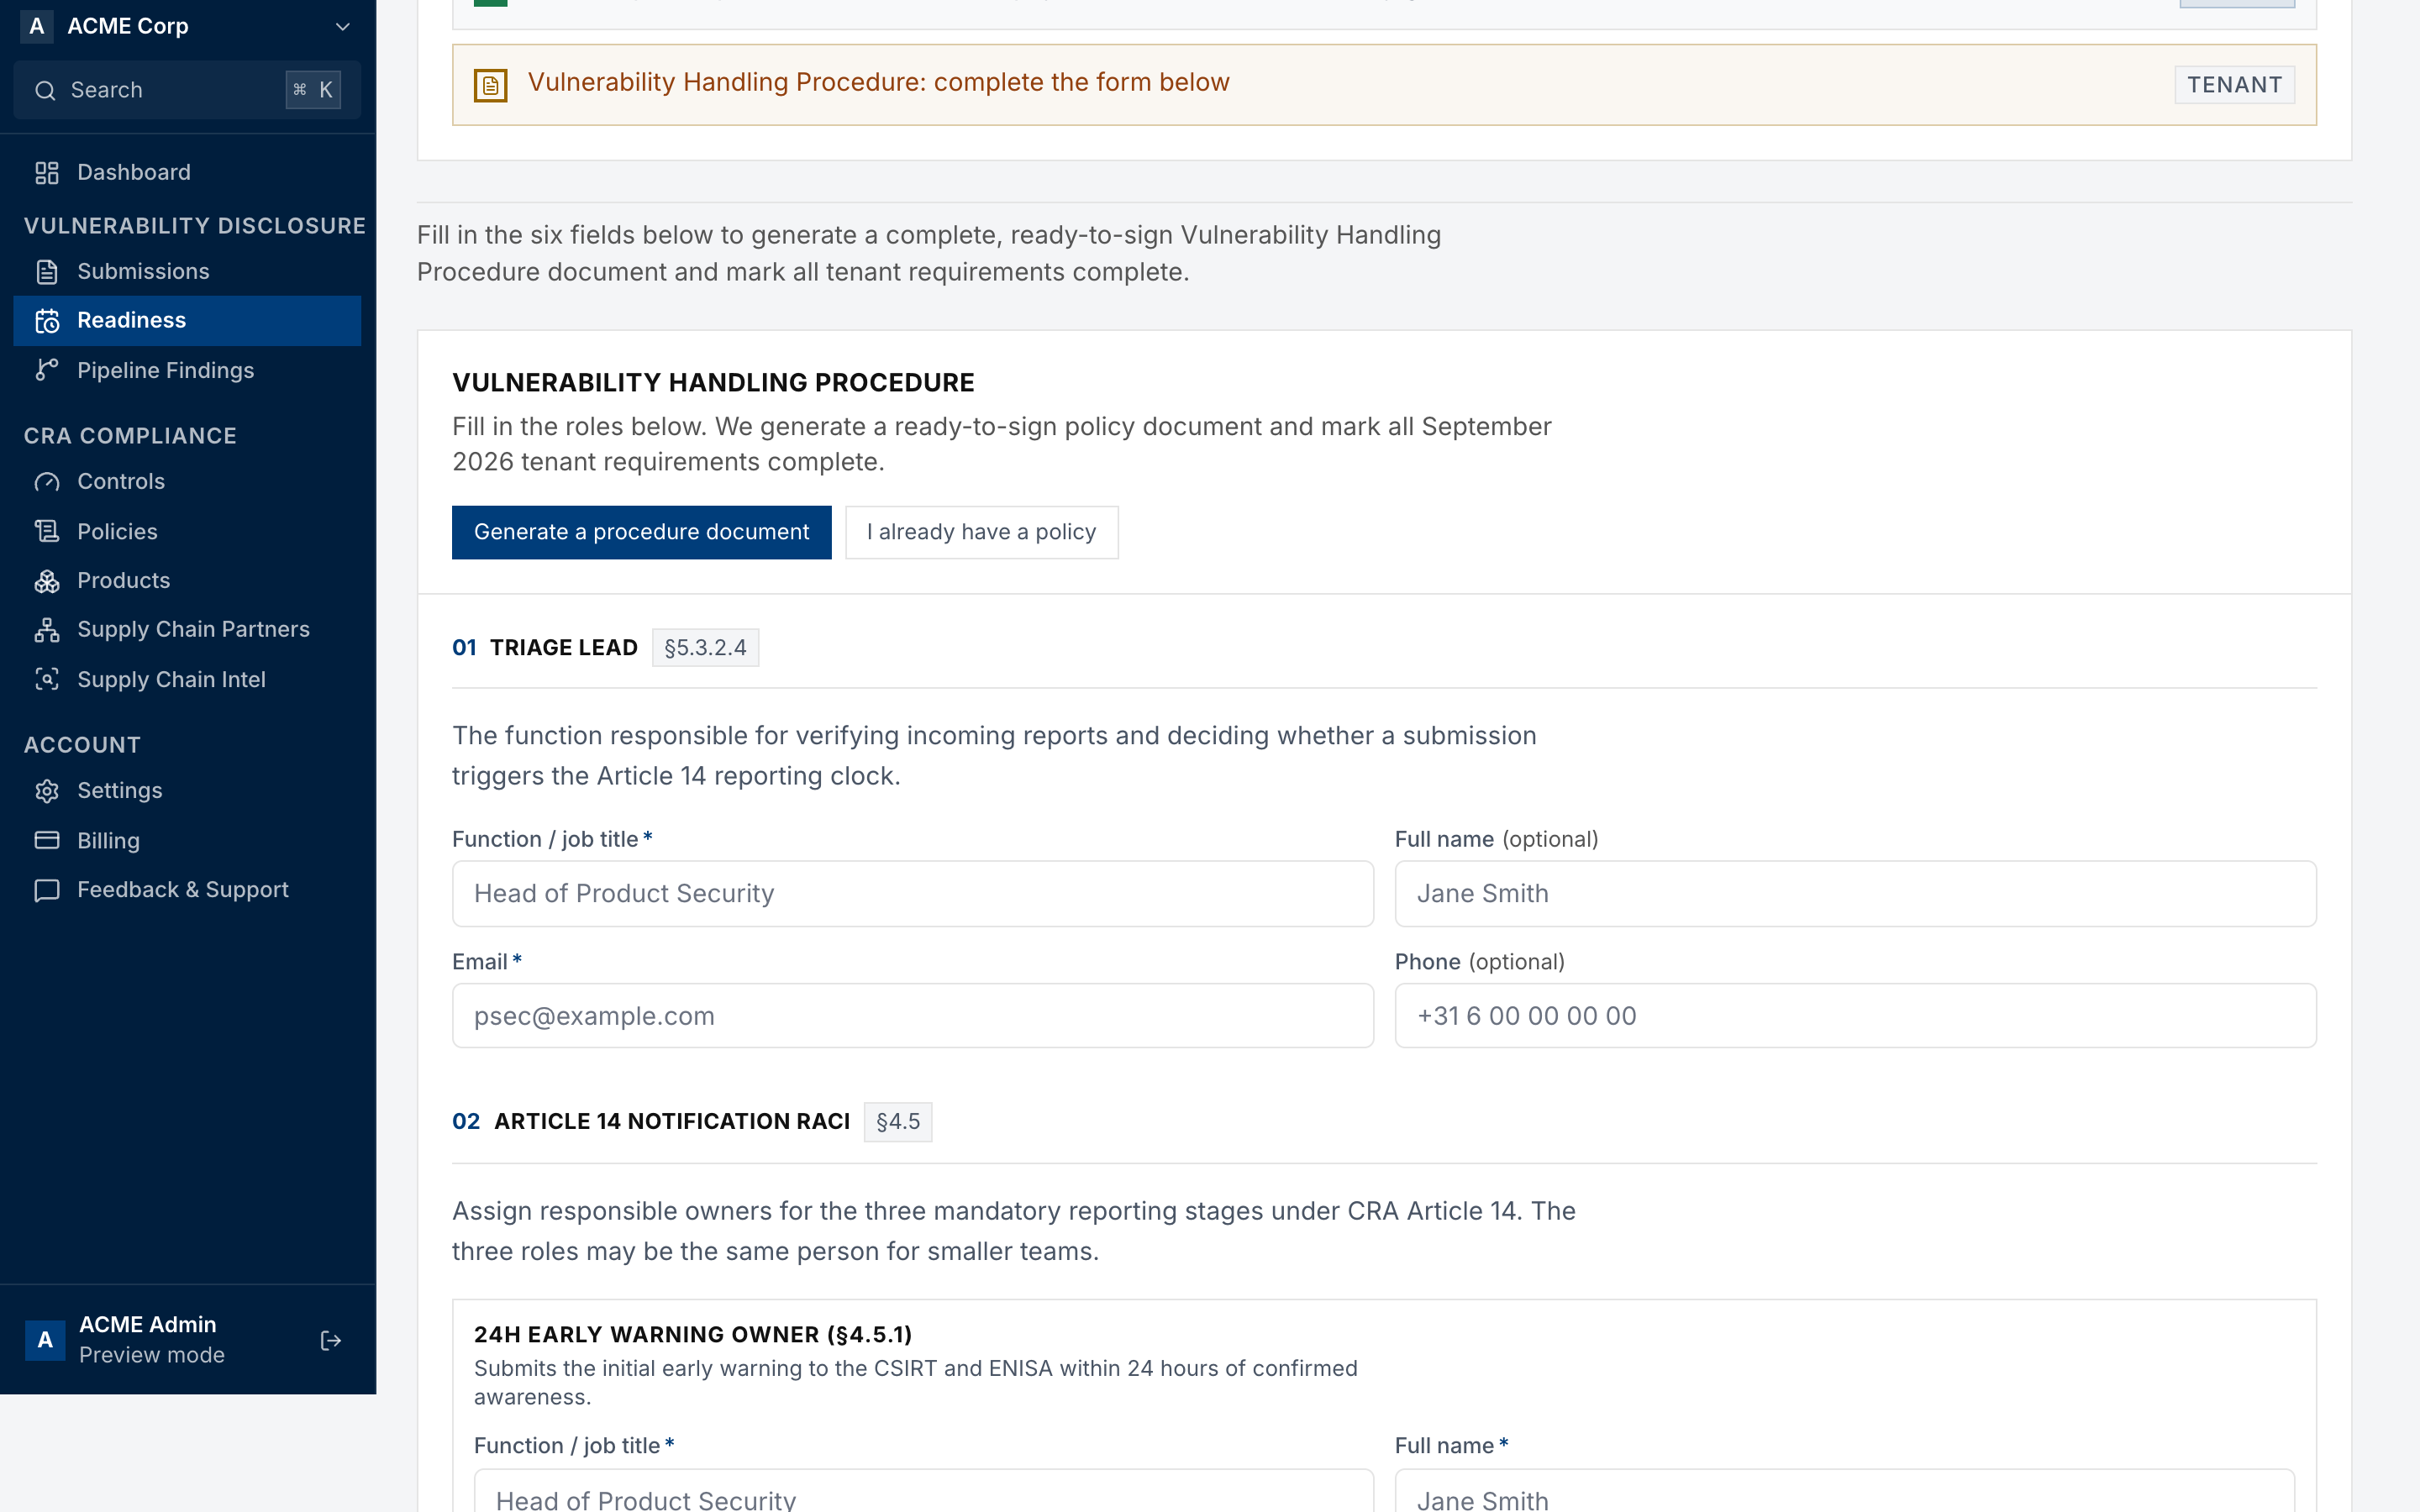
- Select Generate a procedure document. If you already have a signed policy, select I already have a policy.
- Under 01 Triage lead, enter the function and email of the person who verifies reports.
- Under 02 Article 14 notification RACI, assign an owner for the 24-hour early warning, the 72-hour notification and the final report. One person can hold all three roles in a small team.
- Complete the other fields.
- Click Save & Generate Document. With an existing policy, the button is Mark complete.
With I already have a policy, the form asks for the policy reference first. The Article 14 RACI, the awareness procedure and the SRP readiness sections follow it, numbered 01 to 03. They are optional on this path, and the reference alone saves. Fill them in to meet the three Article 14 controls that they feed.
Under the form, Article 14 controls shows which of these three controls your next save meets, and what is missing for the others:
- Article 14 notification RACI assigned
- Vulnerability awareness procedure documented
- Single Reporting Platform (SRP) readiness confirmed
Done when. The procedure is saved. The generated document must be signed by an authorised officer. Keep it with your technical documentation (Article 31). After the save, the 04 Reporting card on Controls counts each of the three controls that the list showed as met. While one of the three is still open, the Readiness overview says how many under Vulnerability Handling Procedure. The saved procedure still counts toward the September 2026 percentage.
Step 3. Publish reporting channel
On the same page, go to Publish your reporting channel.
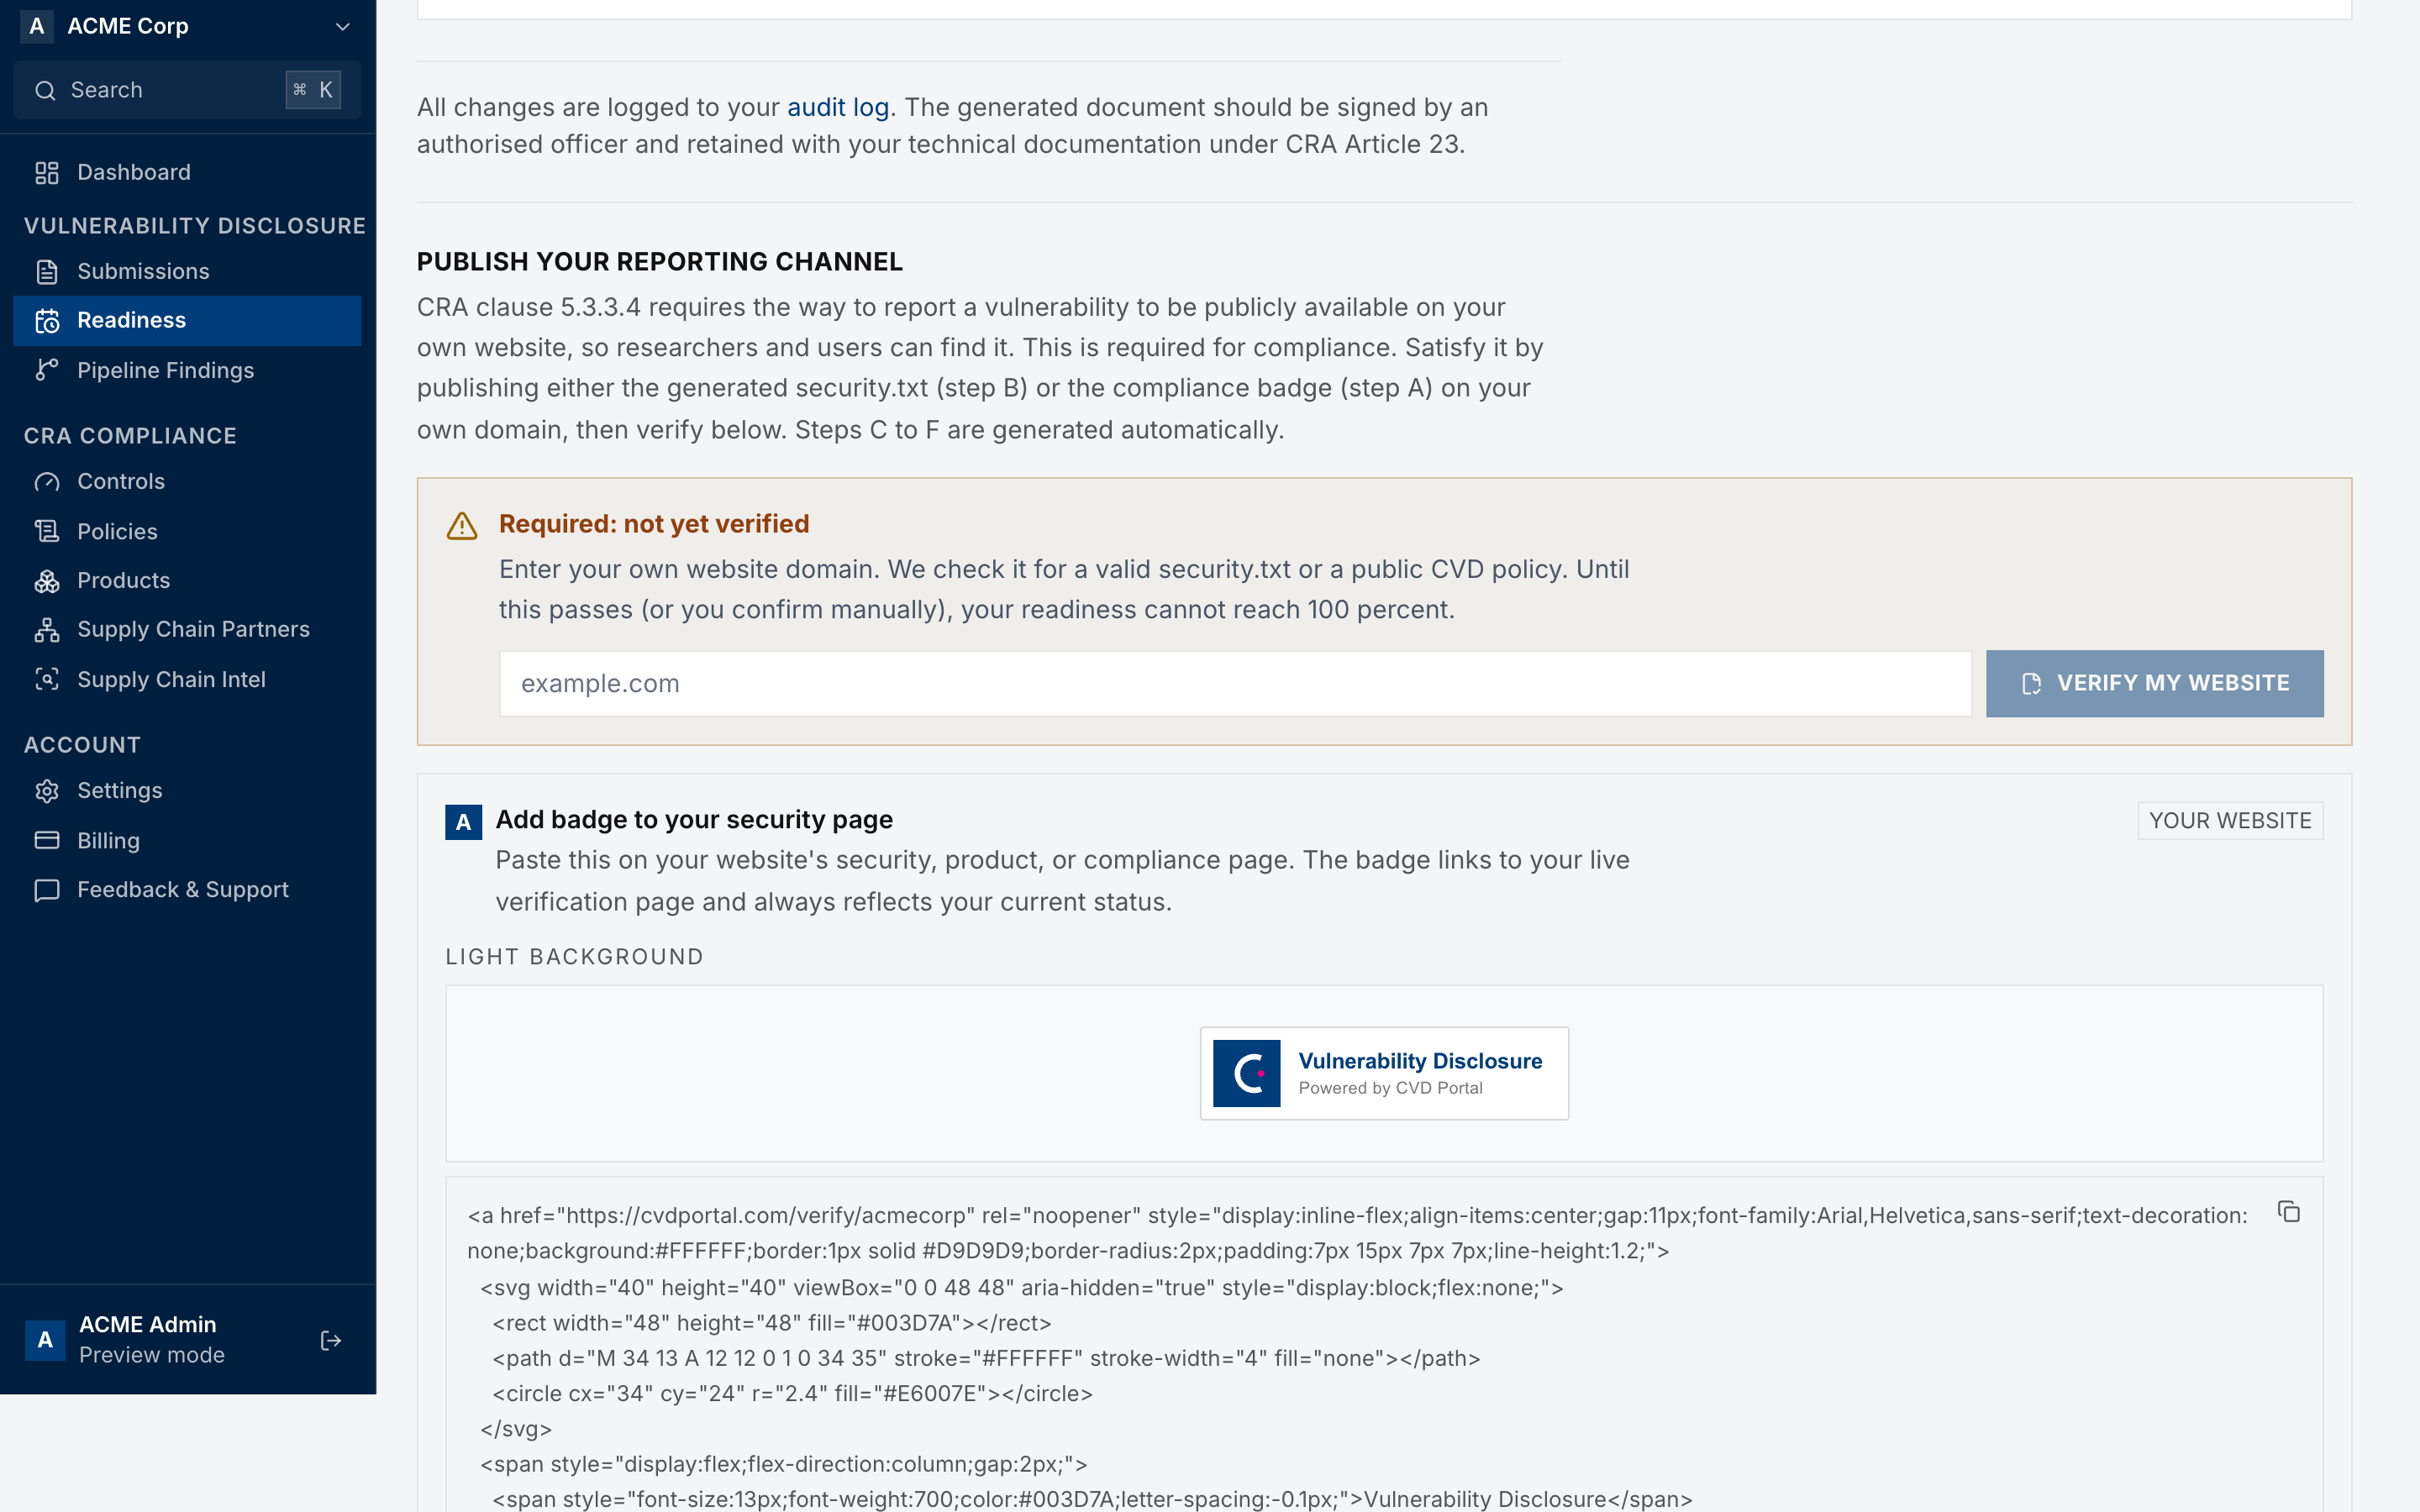
- Publish the generated security.txt, or the compliance badge, on your own website.
- Enter your website domain.
- Click Verify my website. The portal checks the domain for a valid security.txt or a public CVD policy. It also checks that the domain belongs to your company. The domain passes when it is your company email domain, a verified single sign-on domain, or a subdomain of one of these. It also passes when a
ContactorPolicyline in its security.txt names your portal or an address on your company email domain. The generated security.txt has these lines. If none of these is possible, add the DNS TXT record that the check shows, then verify again. - If the scanner cannot reach your site, confirm manually with I confirm I have published it.
Done when. The channel is verified or confirmed. The CRA requires a contact address for reporting vulnerabilities (Annex I, Part II, point 6). EN 40000-1-3 clause 5.3.3.4 expects that channel to be public.
Step 4. Submission alerts
Open Settings, then Notifications.
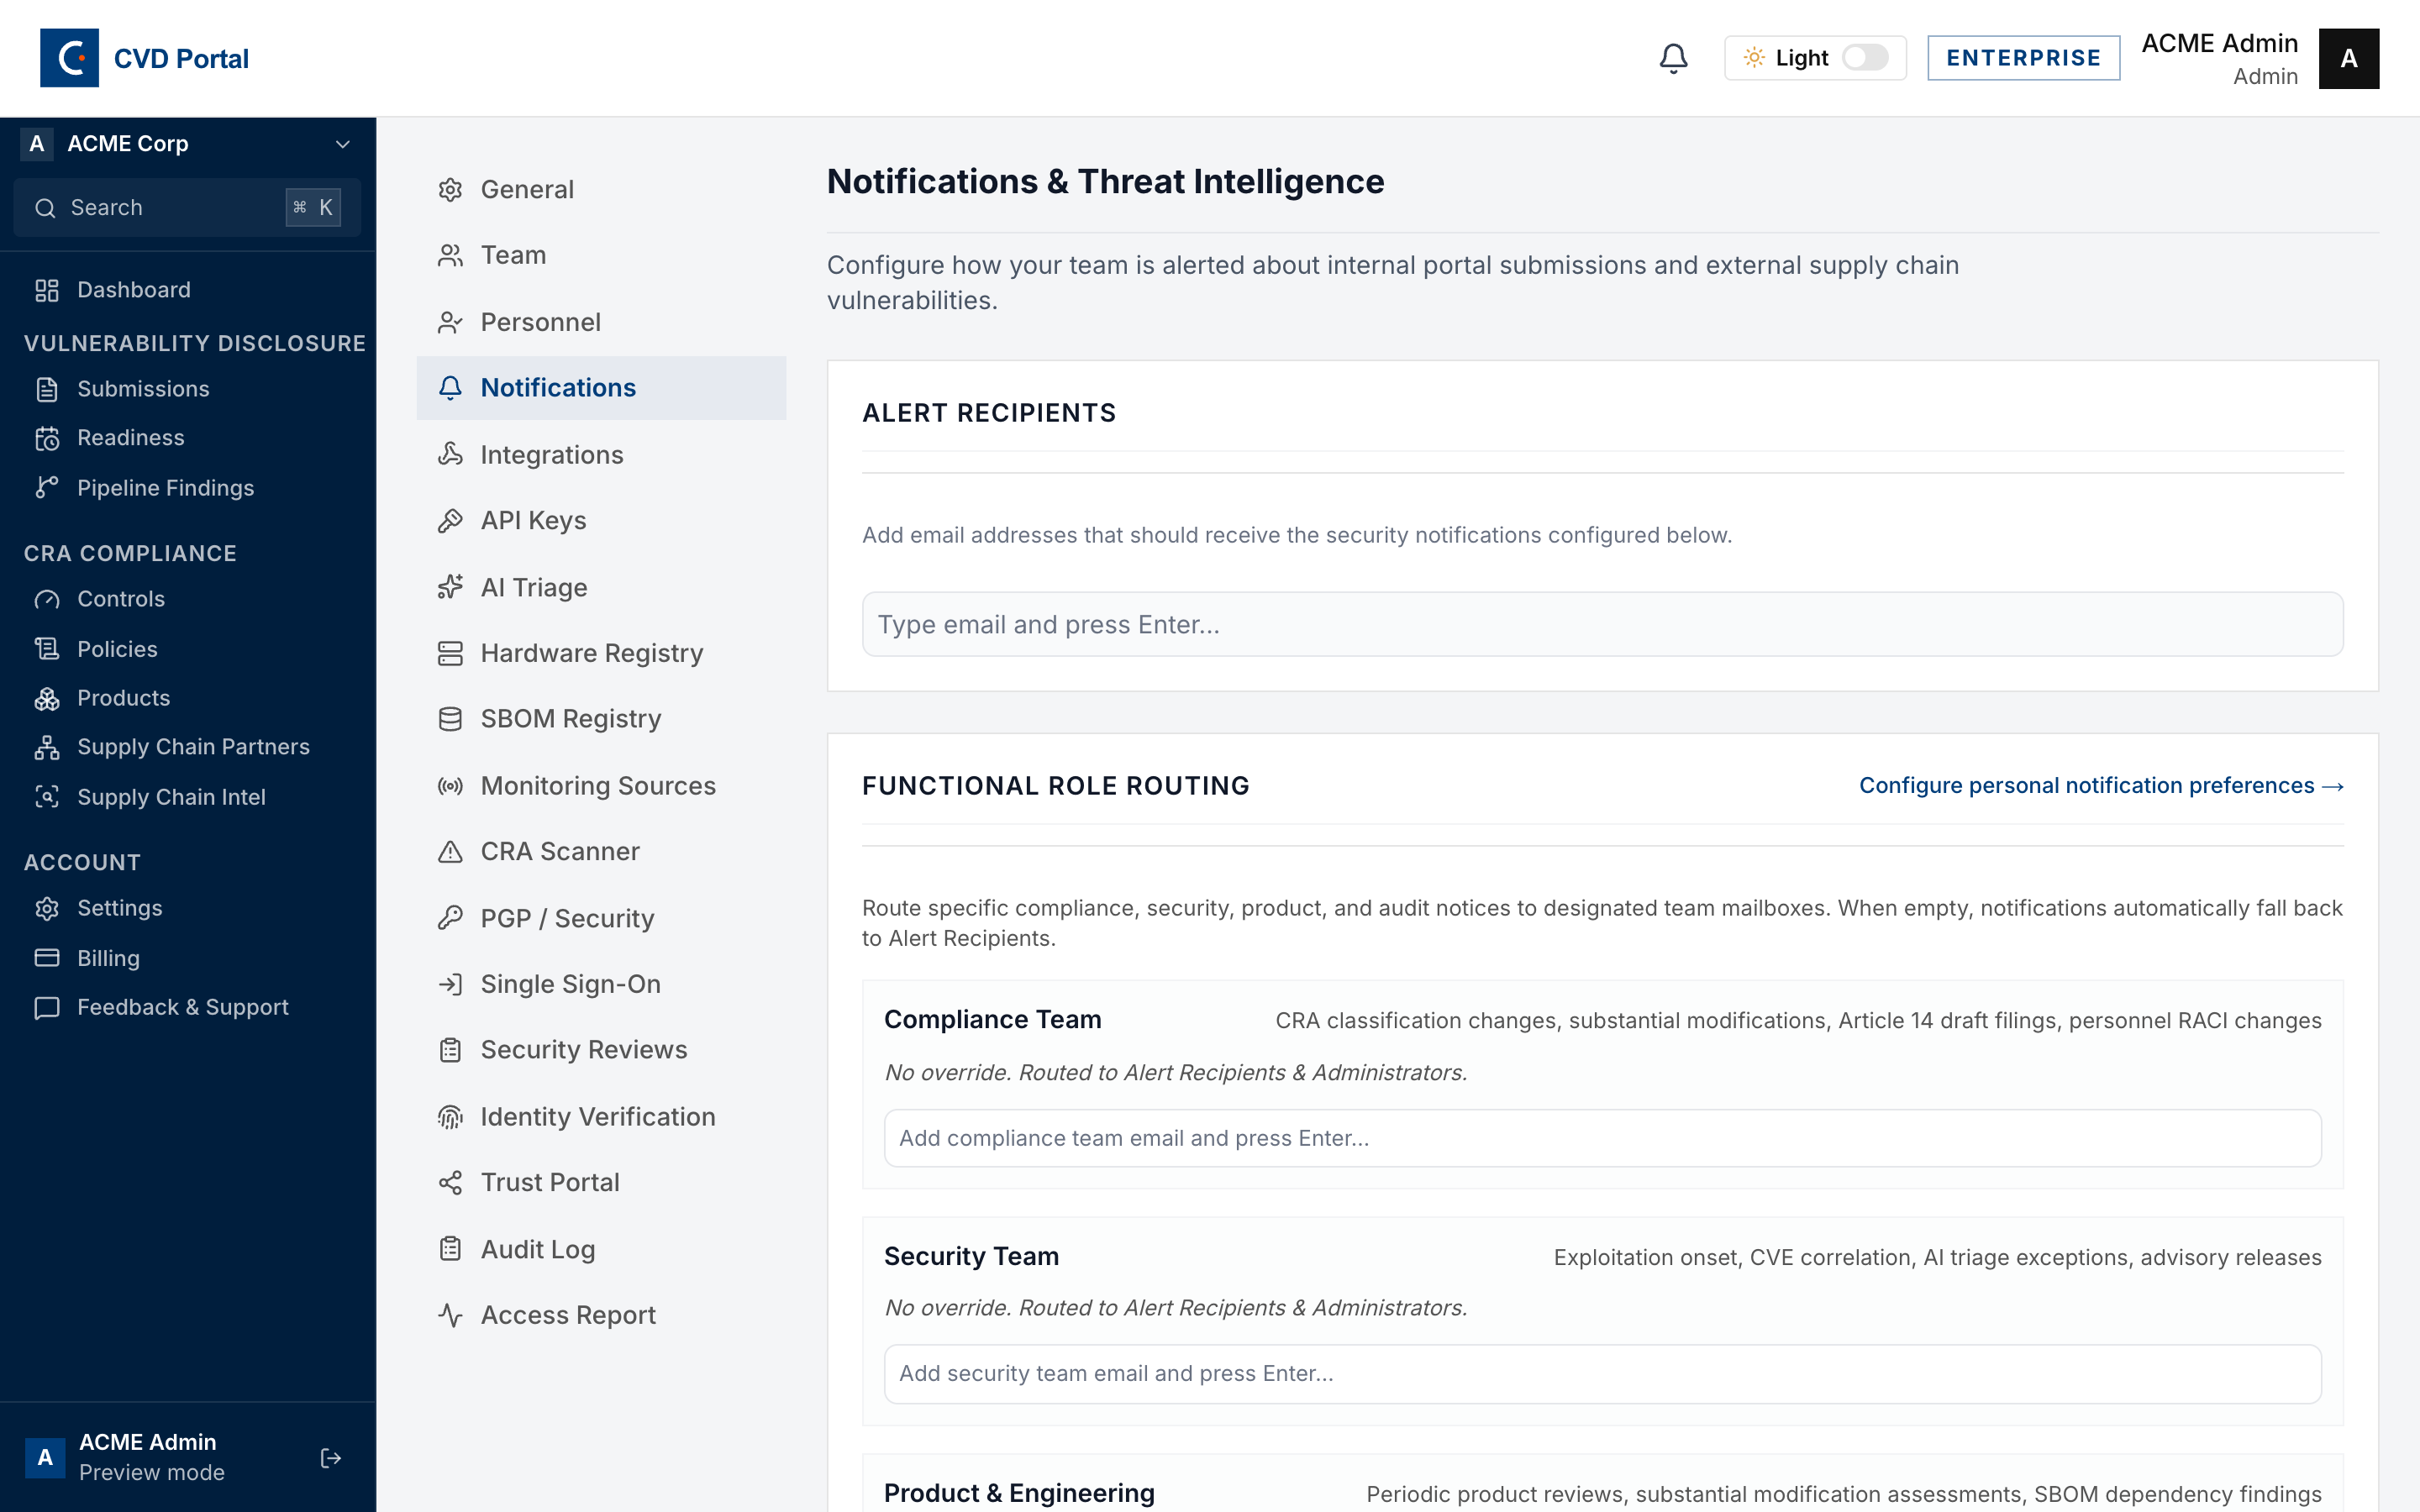
- Under Alert recipients, type each email address and press Enter. Use a shared inbox that someone reads every day.
- Under Functional role routing, add a mailbox for each team if you want to route notices by topic. If you leave a team empty, its notices go to the alert recipients.
- Click Save Preferences.
Done when. Your preferences are saved, New Vulnerability Reports is on, and at least one address gets the alert. Until you save, new-report alerts go to every admin and member of the workspace. A report that nobody sees cannot meet the 24-hour Article 14 clock.
Step 5. Invite your team
On the Free plan, an account has one member, so this step is not in the setup list. Skip to the next step.
Open Settings, then Team.
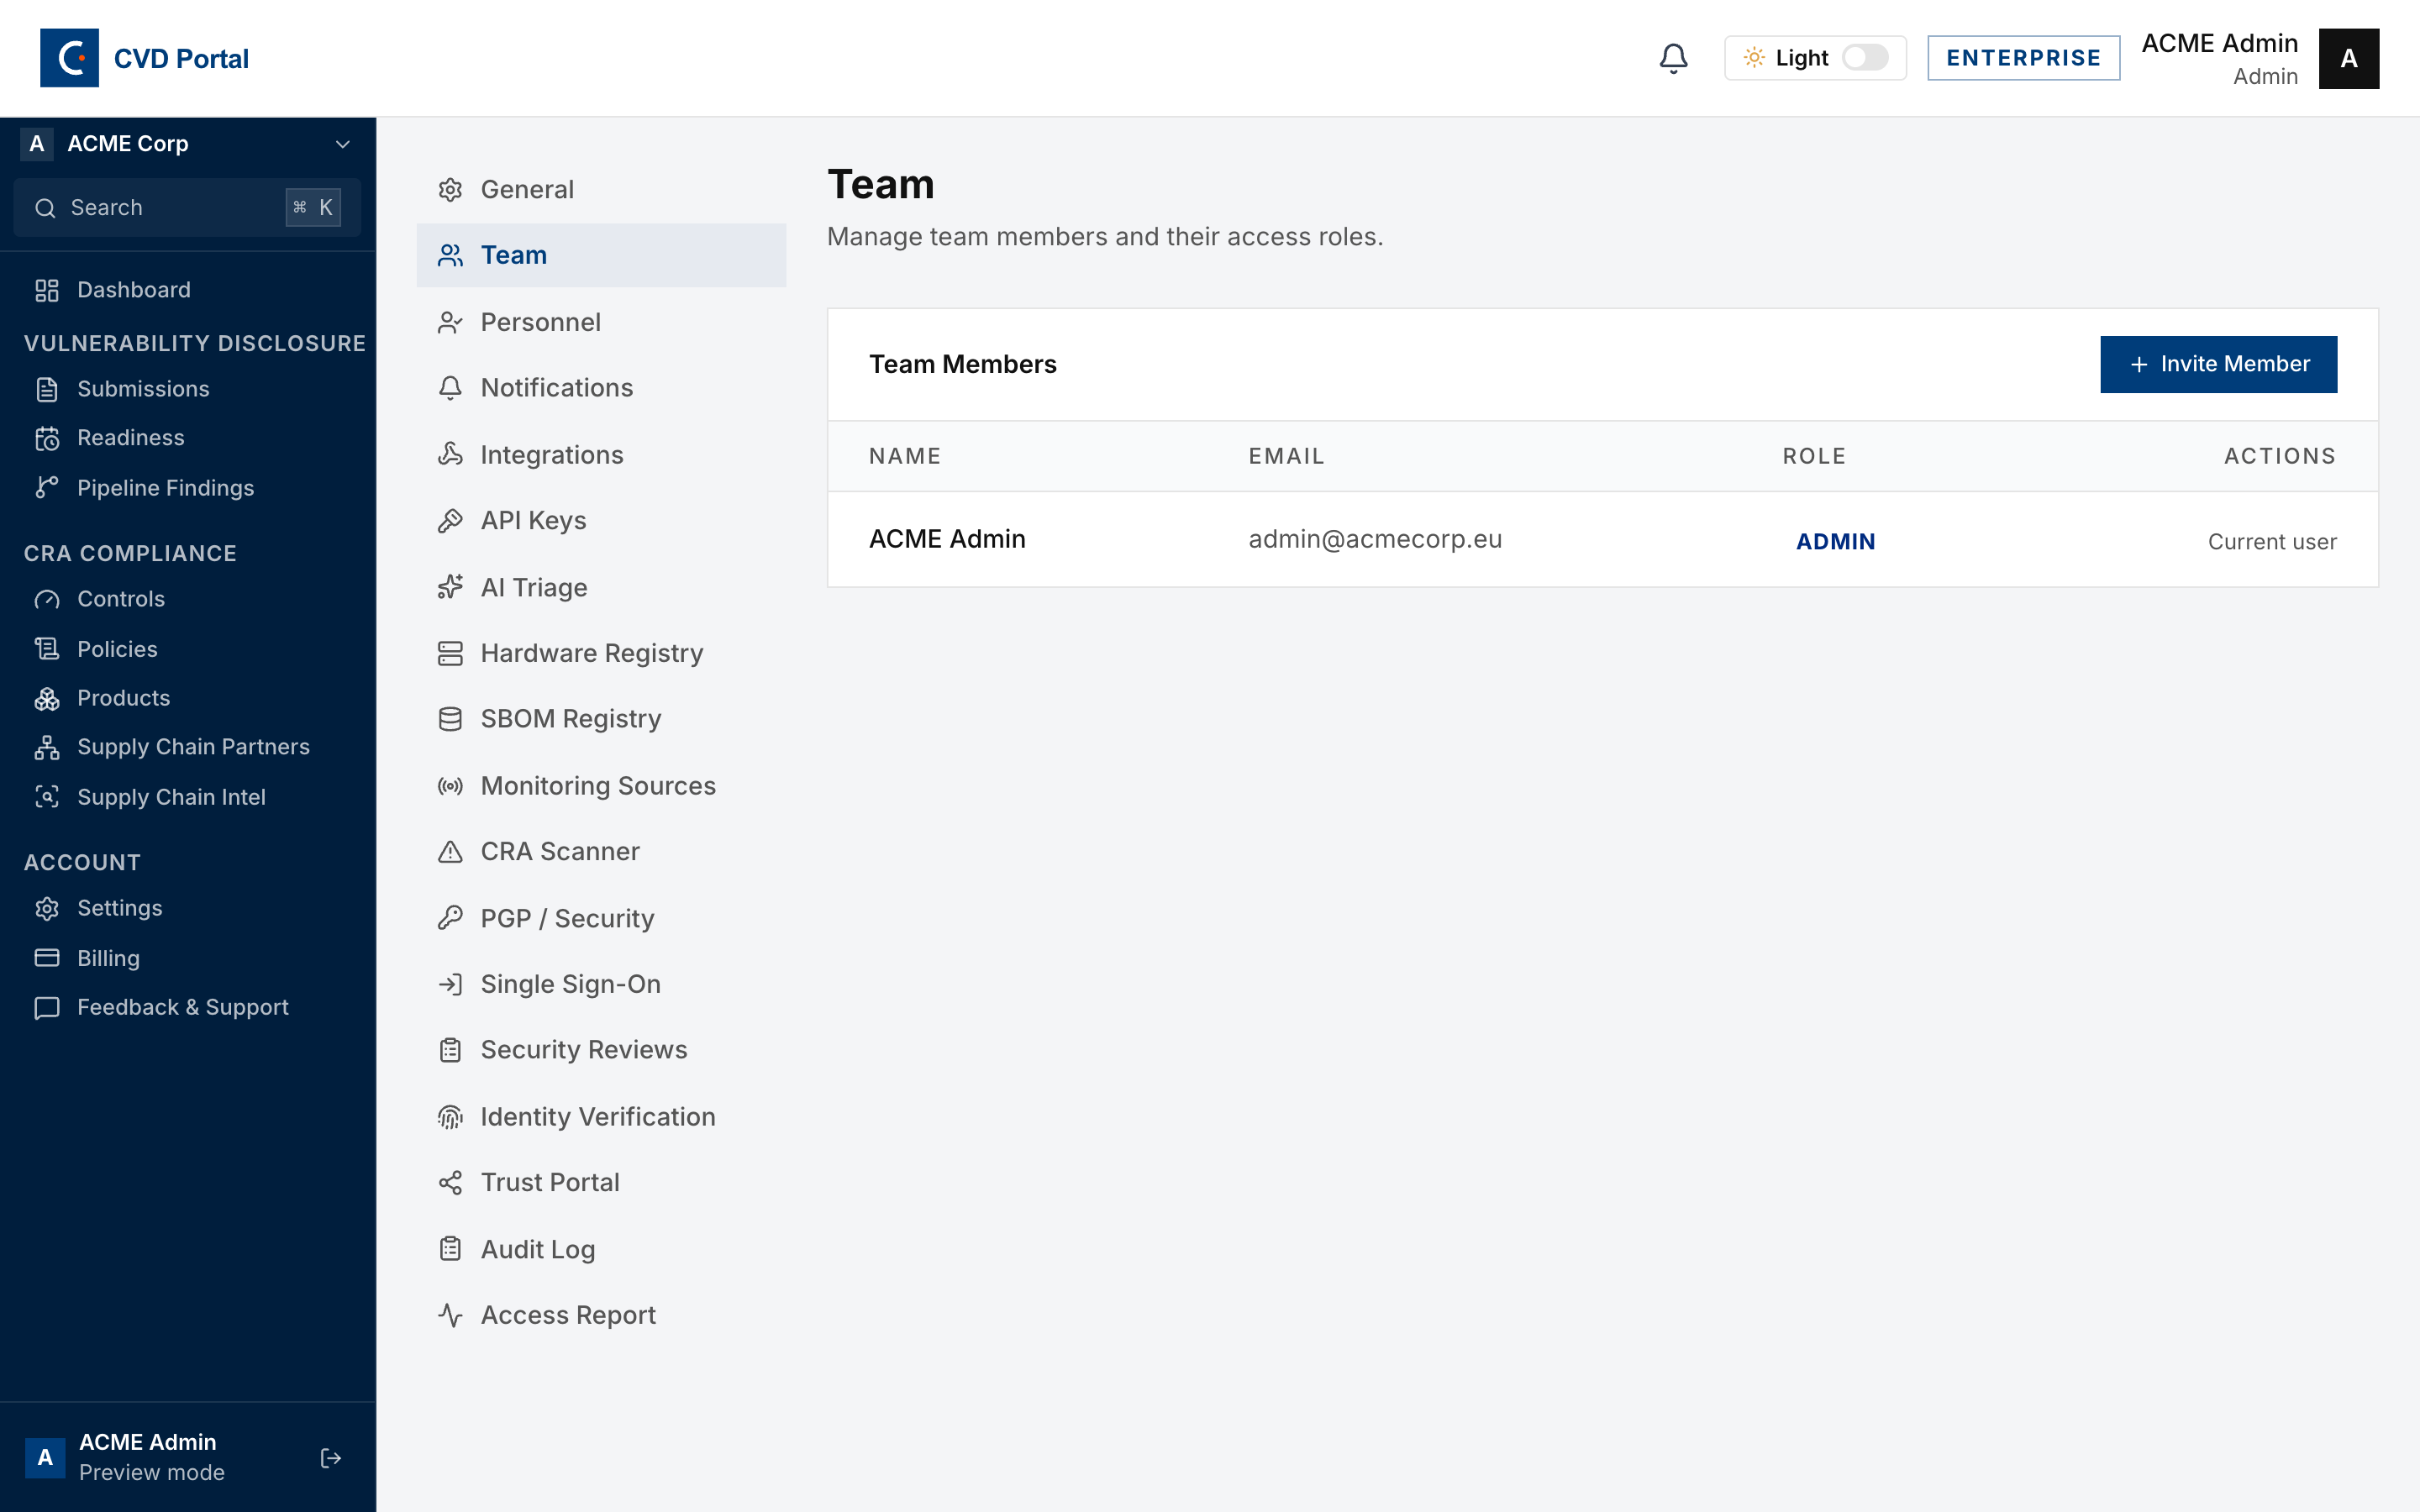
- Click Invite Member.
- Enter the email address.
- Select a role. Member can read and triage. Admin has full control. Auditor is read-only for a limited time.
- Click Send Invitation.
Done when. A second Admin or Member accepts the invitation. An auditor does not count, and an invitation that waits does not complete the stage. Invite at least one other person who can triage, so that a report does not wait while one person is away.
Step 6. First report received
Your public portal is live at https://<your-slug>.cvdportal.com/submit. The Public portal link on the Overview opens it.
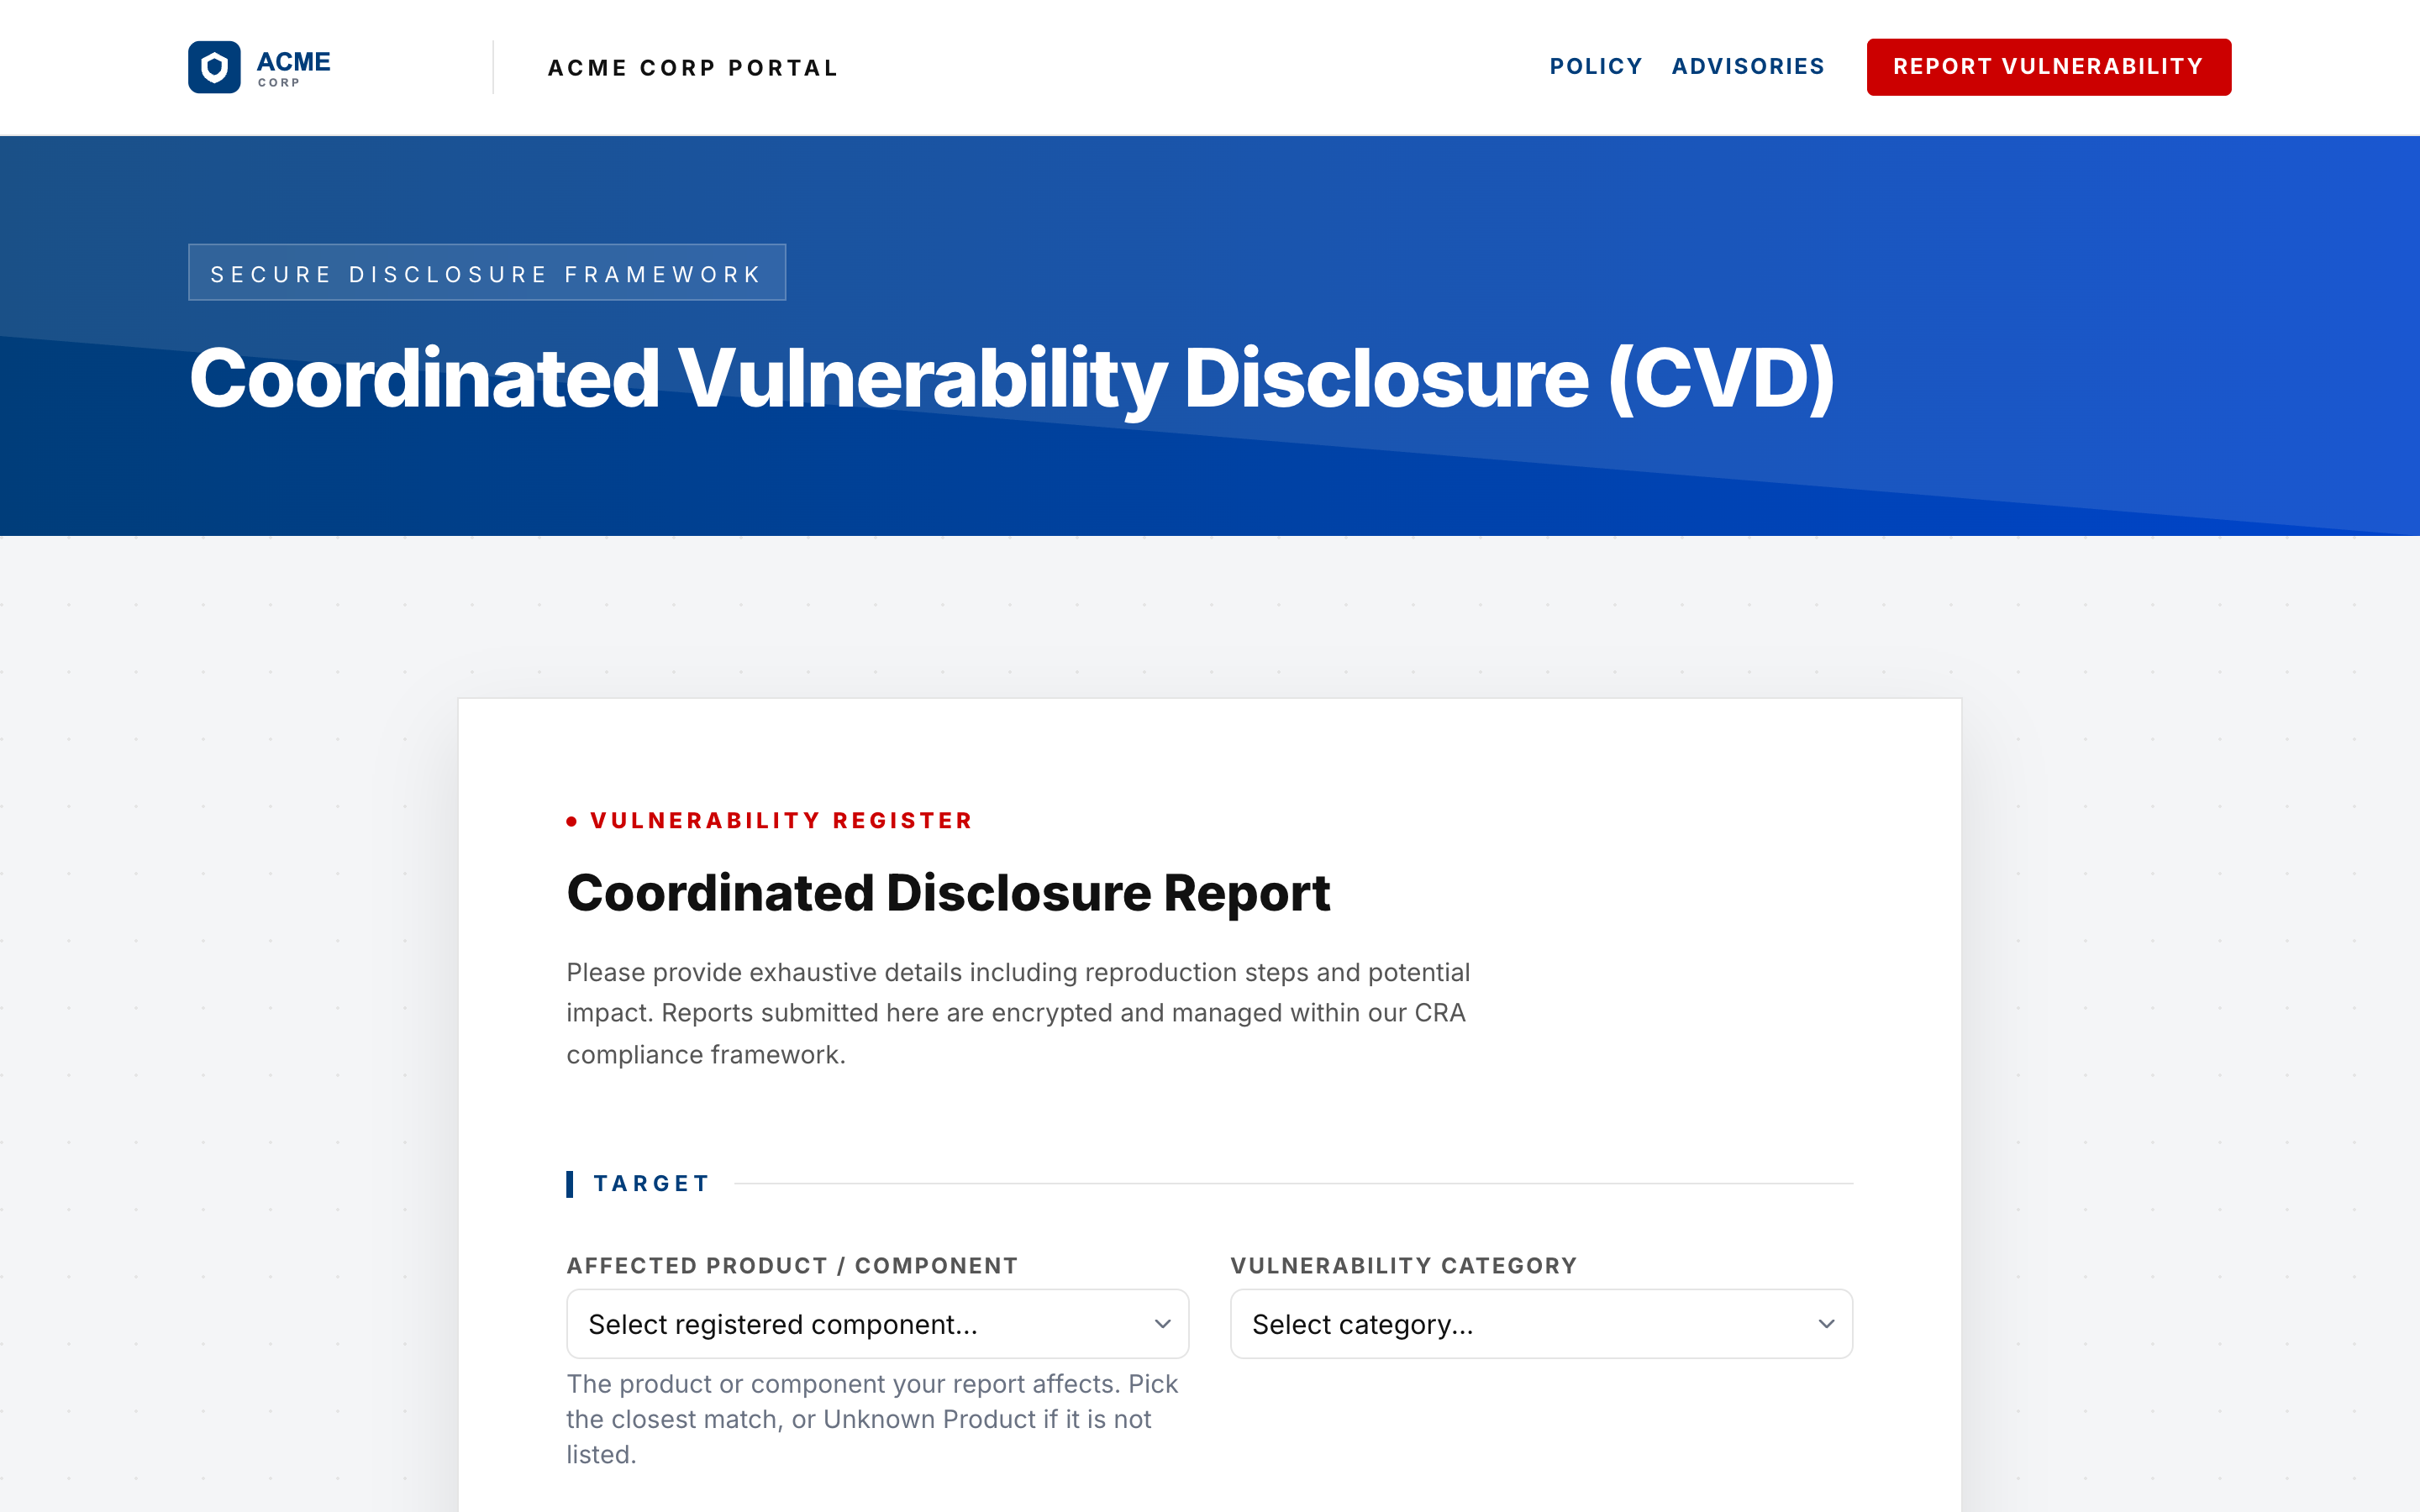
- Link to the portal from your security.txt, your website and your product documentation.
- To test it, submit one report yourself. Mark it as a test in the description.
Done when. The workspace has received at least one report. To work that report, use SOP-10.
Completion checklist
- Article 14 details resolve to a national CSIRT
- Vulnerability Handling Procedure saved, signed and filed
- Reporting channel published on your website and verified
- Alert recipients saved
- At least one other team member accepted the invitation
- At least one report received
- The Company setup row no longer shows on the Overview